Navigate the Series
Coming Soon
Coming Soon
Coming Soon
Coming Soon
If your small business works with the Department of War(DoW) or a major DoW contractor (a “Prime”), you are an official part of the Defense Industrial Base (DIB) as it has historically been called.
Congratulations! You are doing vital work for national security.
But here’s the cold, hard truth: You are a target.
No, not me. I’m I have no classified data anyone would want – you may think.
But you have connections and access.
Organized crime groups and state-sponsored hackers (the bad guys who want to hurt our. Country) don’t start by attacking large Primes like Lockheed Martin or Raytheon directly—it’s too hard.
Instead, they look for the weakest link in the supply chain. Sadly, that weak link is often a small business with fewer resources and less time to focus on security.
Attackers use small businesses as stepping stones to reach the big defense secrets.
58% of cyber incidents impacting major government contractors involve a third-party attack vector—more than double the global average. This demonstrates how vulnerable the entire defense industrial base is to breaches that originate with small- and mid-sized suppliers. (Source: SecurityScorecard Report: Defending the Federal Supply Chain)
The Cybersecurity Maturity Model Certification (CMMC) didn’t appear out of thin air.
In fact, until recent years, DoW spokespeople were quite reluctant to force security measure auditing onto their contractors.
Instead, CMMC is a direct response to a decade of devastating cyber espionage against the U.S. defense supply chain.
Here are a few of the most damaging examples that led Congress to mandate that DoW come up with some framework:
Image Source: Jetline Marvel YouTube
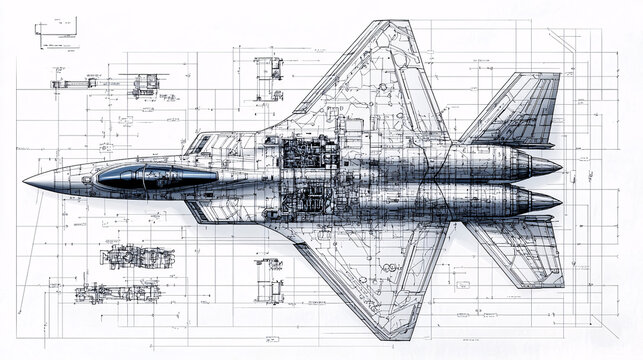
Hackers, widely believed to be working for the Chinese government, targeted multiple defense contractors to steal the technical designs for the F-35 Joint Strike Fighter—the U.S. military’s most advanced stealth aircraft.
While the Primes were hit hardest, the initial access often came through smaller partners who had parts of the design.
This breach saved foreign adversaries billions in R&D and accelerated their own next-generation fighter programs.
The Cost: Loss of technological edge on the battlefield and billions in taxpayer money.
In 2018, hackers tied to the Chinese government infiltrated a U.S. Navy contractor’s unclassified network and stole over 614 gigabytes of highly sensitive data.
This trove included information related to the Sea Dragon project—secret plans for a submarine-launched supersonic anti-ship missile that was crucial for the United State’s defense of Taiwan.
The incident was a direct result of CUI being inadequately protected on a sub-contractor’s unclassified system.
Though not strictly a DoW breach, the compromise of the Office of Personnel Management (OPM) exposed the personal data, including fingerprints and background check information (SF-86 forms), of over 21 million federal employees, contractors, and their families.
This data is invaluable for foreign intelligence agencies to identify, track, and potentially compromise U.S. personnel and spies.
The Lesson: Even personal data is a national security asset.
After this decade of failure, the DoW realized it couldn’t just ask its contractors to be secure; it had to mandate and verify it. That’s the core purpose of CMMC.
You may truly believe you have “no classified data anyone would want.”
And you’re right—you probably don’t handle Top Secret blueprints or nuclear codes.
But you still have something that adversaries want.
The information you handle is still valuable and easier for adversaries to steal: Controlled Unclassified Information (CUI).
CUI is sensitive government-owned or government-generated data that, while not classified, still requires protection due to law, regulation, or government-wide policy.
Think of it this way: Classified information is locked in a vault, but CUI is the detailed map of the vault, the combination’s first two digits, and the guard rotation schedule.
Attackers don’t need the final secret; they need the thousands of unclassified pieces that, when stitched together, reveal the whole picture.
What exactly are these pieces of CUI that small and mid-sized businesses (SMBs) in the Defense Industrial Base (DIB) handle? They are the essential, daily details of defense projects:
Controlled Technical Information (CTI): This is the most common CUI handled by DIB companies. It includes engineering drawings, specifications, technical reports, manufacturing instructions, source code, and research data. For example, the detailed performance requirements for a single component on a new radar system or the precise milling tolerances for a piece of aircraft hardware.
Proprietary Business Information: Procurement schedules, vendor lists, pricing data, and pre-decisional budget information.
Personnel and Security Information: Personally Identifiable Information (PII) of government employees or contractors, and security-related details for a facility.
Export-Controlled Information: Data that falls under regulations like the International Traffic in Arms Regulations (ITAR) or Export Administration Regulations (EAR).
The cumulative loss of this CUI allows foreign adversaries to achieve several strategic goals:
Reverse Engineering: They can shortcut billions in R&D by simply reading the design, testing, and manufacturing details of a component you created.
Supply Chain Vulnerabilities: They identify which small businesses are the easiest to hack to gain initial access, effectively mapping the entire defense supply chain’s weak points.
Economic Advantage: They can replicate U.S. technology faster and cheaper, challenging the American technological edge globally.
The historic breaches—like the F-35 blueprint heist which involved smaller partners—proved that relying on Primes alone to secure the data wasn’t working.
The security chain is only as strong as its weakest link, and for years, that link was the unverified self-attestation of security by subcontractors.
CMMC is the Department of War’s official, mandated fix.
It moves the DIB away from self-policing to a model of verification.
By requiring a CMMC certification, the government is ensuring that every single business, down to the smallest subcontractor, is implementing the required cybersecurity controls to protect the small pieces of CUI that, together, create national defense secrets.
It’s no longer just a good idea; it is a non-negotiable requirement to participate in the DIB.
Your compliance is directly linked to national security and your ability to win future contracts.
In the next article, we will discuss the two types of data that CMMC deals with and how they determine your CMMC level.